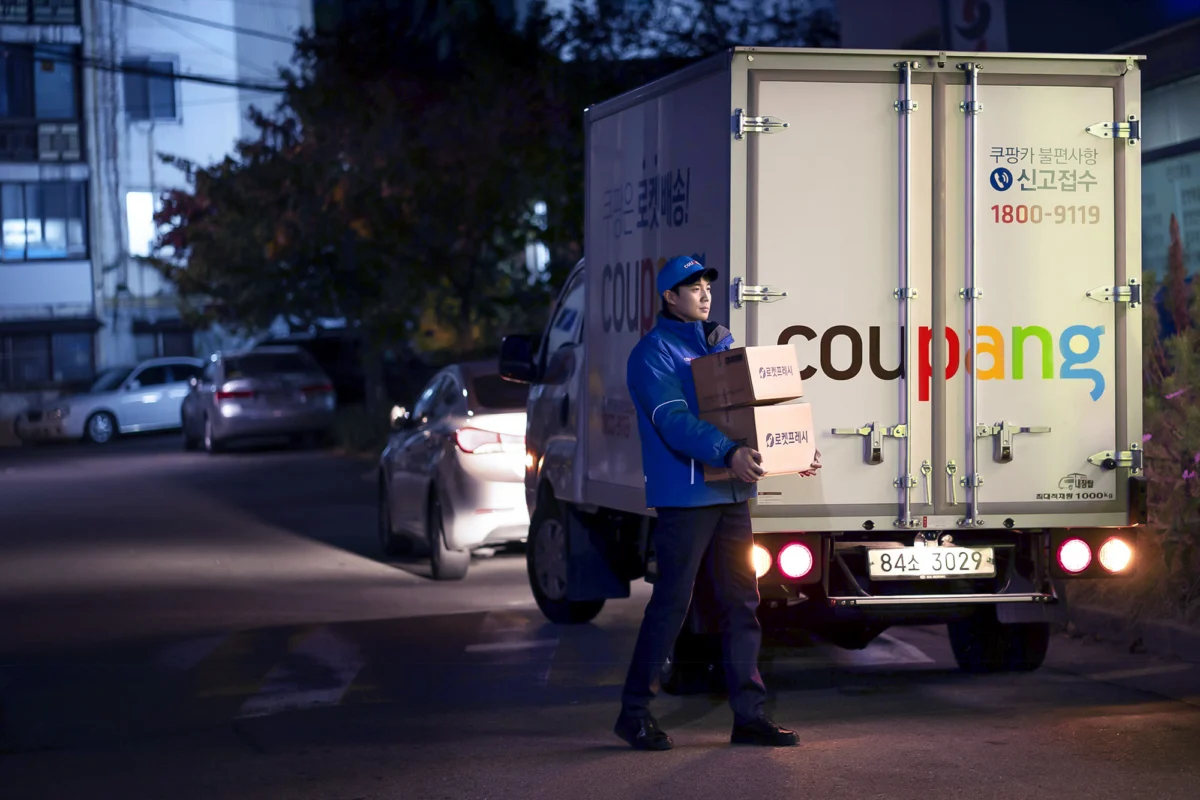
South Korean regulatory authorities have delivered an unprecedented financial penalty to retail behemoth Coupang, handing down a record-shattering fine of 624 billion won, equivalent to more than $400 million USD. This severe disciplinary action comes in the wake of a catastrophic cybersecurity failure discovered late last year, which compromised the sensitive personal information of over 34 million customers—representing roughly two-thirds of the entire South Korean population.
The decision, finalized and announced on Thursday by Seoul’s Personal Information Protection Commission (PIPC), represents the maximum possible statutory penalty under national data privacy frameworks. It also underscores a growing international willingness by regulators to hold multinational technology and retail corporations strictly accountable for safeguarding consumer data. However, the ruling has quickly escalated beyond a domestic regulatory dispute, triggering diplomatic friction between Seoul and Washington over the treatment of United States-headquartered corporations operating abroad.
The Scope and Nature of the Breach
The security failure at Coupang, often colloquially referred to by market analysts as the "Amazon of Asia," is among the largest corporate data leaks in South Korean history. According to forensic findings disclosed during the regulatory investigation, the months-long unauthorized data exposure allowed a former employee to systematically siphon off vast repositories of confidential consumer records.
The compromised dataset was comprehensive, exposing high-risk personal identifiers that leave victims uniquely vulnerable to targeted phishing campaigns, identity theft, and financial fraud. Specifically, the leaked information included full customer names, private email addresses, physical shipping destinations, personal telephone numbers, and exhaustive historical records of consumer purchases. Because Coupang commands a near-ubiquitous presence in South Korean daily commerce, the breach effectively affected a staggering demographic breadth, touching nearly every household in the country.
The sheer volume of exposed data alarmed privacy advocates and lawmakers alike, who pointed out that modern e-commerce platforms hold systemic importance to national infrastructure. When companies of Coupang’s scale fail to implement rigorous internal access controls, the resulting fallout compromises macroeconomic trust in digital marketplaces.
Chronology of Events
To understand the gravity of the PIPC’s penalty, it is essential to trace the timeline of the investigation, the discovery of the breach, and the subsequent geopolitical fallout.
- Early to Mid-2025: The unauthorized data exfiltration begins internally, driven by lax internal access monitoring that allows a former employee to bypass standard data protection barriers and harvest consumer registries over a sustained period.
- December 2025: Coupang officially detects the security breach and formally reports the incident to South Korean regulatory authorities, initiating a comprehensive government-led forensic investigation into the root causes and the total volume of compromised files.
- Early 2026: Investigators from the PIPC map the full extent of the leak, confirming that over 34 million accounts were compromised. Concurrently, criminal and civil inquiries target executive accountability, leading to heightened scrutiny from South Korean legislators regarding corporate governance at the retailer.
- April 2026: Reports emerge indicating that U.S. representatives are intervening on behalf of the American-headquartered firm. Lawmakers in Washington allegedly link the handling of the Coupang investigation and executive probes to broader bilateral trade and diplomatic ties, prompting sharp rebukes from South Korean parliamentarians.
- Current Date: The PIPC officially issues the record-shattering 624 billion won fine. Coupang publicly announces its intention to aggressively contest and challenge the regulatory verdict through the legal system.
Supporting Data and Comparative Regulatory Context
The 624 billion won penalty is not merely large in absolute terms; it marks a watershed moment in Asian regulatory enforcement. South Korea has progressively strengthened its Personal Information Protection Act (PIPA) over the last decade, endowing enforcement bodies with the authority to levy fines calculated as a percentage of a company’s total global or domestic turnover, rather than relying on nominal, fixed penalties.
By contrast, data privacy enforcement in the United States operates under a fragmented, sector-specific legal regime. U.S.-based technology and retail companies rarely face financial sanctions or criminal prosecution of this magnitude for consumer data breaches, primarily due to the absence of a comprehensive federal privacy law and weaker enforcement mechanisms at the federal level. While state-level regulators, such as the California Attorney General, and federal agencies like the Federal Trade Commission (FTC) occasionally issue substantial settlements, they rarely approach the punitive severity or direct statutory percentages seen in South Korea or the European Union under the General Data Protection Regulation (GDPR).
This regulatory asymmetry frequently creates friction when foreign jurisdictions attempt to penalize multinational corporations whose parent entities are incorporated in the United States. While European regulators have routinely issued multi-million-dollar fines against Silicon Valley giants, Asian markets are increasingly asserting their sovereign right to enforce stringent local compliance standards, regardless of a firm’s corporate domicile.
Official Responses and Corporate Posture
In the wake of the PIPC’s announcement, affected parties have staked out firm positions that signal a protracted legal and diplomatic battle ahead.
Coupang has maintained a defensive posture, confirming to international media outlets, including BBC News, that it intends to formally challenge the regulatory decision in court. The company has previously emphasized its commitment to enhancing its cybersecurity posture and cooperating with authorities, but it argues that the penalty is disproportionate to the actual harm demonstrated and fails to account for the malicious intent of an isolated bad actor within its workforce. Legal experts suggest that Coupang’s defense strategy will likely focus on questioning the legal interpretation of statutory thresholds and arguing that the company acted responsibly upon discovering the internal breach.
Conversely, South Korean regulatory officials have defended the penalty as a necessary deterrent. The PIPC maintains that a firm entrusted with the personal data of the vast majority of the nation’s populace bears an absolute fiduciary and legal responsibility to maintain impenetrable access controls.
The Diplomatic Dimension
The controversy has notably spilled over from the courtroom into the halls of international diplomacy. The involvement of U.S. political figures has introduced a complex geopolitical subplot to what would otherwise be a domestic regulatory enforcement action.
According to reports from financial and political monitors, several U.S. lawmakers have engaged in high-level communications with South Korean officials, purportedly linking the harsh regulatory treatment—and potential criminal probes facing Coupang executives—to the broader state of bilateral relations between Washington and Seoul.
This diplomatic pressure has not been well-received by South Korea’s political establishment. Local lawmakers have openly and sharply condemned what they characterize as unwarranted foreign interference in domestic legal proceedings. South Korean officials argue that foreign entities operating within their sovereign borders must be subject to local laws without facing political intimidation or having commercial accountability subordinated to geopolitical alliances. The dispute highlights the delicate balancing act required when foreign direct investment intersects with national security and consumer protection mandates.
Broader Industry Impact and Strategic Implications
The record fine against Coupang serves as a powerful cautionary tale for multinational corporations operating retail, fintech, and digital platforms across Asia. The implications of this ruling extend far beyond a single corporate balance sheet, reshaping how foreign and domestic firms must approach cybersecurity and risk management.
- Elevated Compliance Costs: Companies can no longer treat cybersecurity compliance as a secondary corporate overhead expense. With penalties scaling into the hundreds of millions of dollars, boardrooms must allocate capital proactively to ensure zero-trust architectures, advanced insider threat monitoring, and rigorous data minimization practices.
- Insider Threat Mitigation: The Coupang breach underscores the reality that external hackers are not the only threat vector. Organizations must implement strict internal data governance, ensuring that former and current employees do not retain unchecked administrative privileges to harvest consumer records.
- Jurisdictional Risk: U.S.-headquartered multinationals expanding into highly regulated foreign markets must recognize that local regulatory bodies are increasingly willing to impose maximum statutory penalties. Relying on diplomatic intervention to mitigate regulatory fallout is becoming an increasingly untenable corporate strategy.
- Consumer Trust Deficit: In highly competitive digital economies, reputational damage can quickly translate into catastrophic market share erosion. While Coupang remains a dominant player in South Korea, the erosion of consumer trust following the exposure of 34 million user profiles opens the door for nimble competitors to capture disgruntled market segments.
Conclusion
As Coupang prepares to challenge the 624 billion won penalty in the South Korean legal system, the case stands as a defining moment for global data privacy enforcement. It highlights the growing tension between national consumer protection mandates and the globalized nature of modern commerce, while setting a formidable benchmark for accountability in the digital age. Whether the penalty is upheld, reduced, or modified on appeal, the regulatory landscape has irrevocably shifted, signaling that lax cybersecurity protocols will no longer be tolerated, regardless of a corporation’s size, origin, or political connections.
